





Game Security · Anti-Cheat · Reverse Engineer · Developer
I work on keeping multiplayer games fair: understanding how cheats actually work, then building the detections that catch them.
Game security & anti-cheat · Windows internals · IDA / Ghidra · detection engineering · SQL & telemetry


I work where game security, low-level systems and detection engineering meet.
That means taking apart how cheats and anti-cheat actually behave — kernel drivers, DMA hardware, aim automation, input emulation — and turning that understanding into detections, telemetry queries and reports a security team can act on. Understanding the attack is the prerequisite; building the defence is the job.
I co-build Decepticon — an autonomous red-team agent with 5.6k+ stars — and Vigilo, an AI researcher for Web3 bounties and audit contests.
Know how the cheat works, and you know exactly what behaviour to measure.
|
Cheat taxonomy for FPS titles, behavioral aim detection, match-integrity analytics, HWID and account-economy abuse, cheat-community intelligence.
|
Static + dynamic analysis of native code, drivers and anti-tamper. Kernel emulation, VT-x research, protocol recovery — the ground truth behind every detection.
|
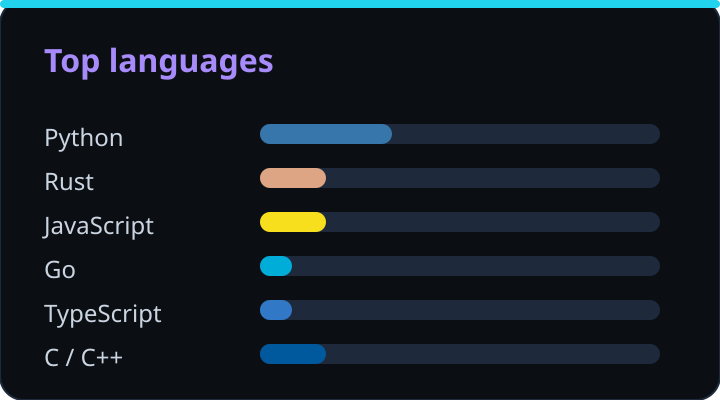
C/C++, Rust, Go, Zig, Python, TypeScript, SQL. Detection pipelines, MCP servers, desktop tooling, embedded Linux.
|
The defence-in-depth stack I build and study — host signals → static signals → behavioral signals → economic/account signals → intelligence.
| Project | What it is |
|---|---|
| apex-anticheat-lab | FPS anti-cheat lab: cheat taxonomy, aim-kinematics detections, match-integrity SQL, YARA, host survey |
| cheat-intel | Cheat-community intelligence: monitoring methodology, trend reports, the intel → detection feedback loop |
| account-security | ATO, credential stuffing, session and identity abuse detection — signal catalogue + SQL + scoring |
| Kevlar | Windows kernel-driver emulation & behavioral analysis (Unicorn) |
| unknowncheats-mcp | Structured access to public cheat-community research threads |
How I work on a cheat problem:
- Taxonomy first — name the class (aimbot / triggerbot / ESP / DMA / macro / spoofing / boosting) and which detection layer it can possibly show up in.
- Behaviour over binaries — signatures expire in days; aim kinematics, input timing and economic behaviour survive cheat rewrites and hardware changes.
- Cohort before score — mouse vs. controller, rank tier, weapon class. A pooled baseline produces false positives, not detections.
- Explainable, ranked review — never auto-ban on one feature. Every flag carries the numbers that produced it.
- Measure the enforcement — infection rate before/after a wave, and how fast the adversary adapts. Tempo is the real KPI.
| Project | What it is | |
|---|---|---|
| Decepticon | Autonomous red-team agent — authorized assessments, RoE-aware execution |  |
| Vigilo | AI researcher for Web3 / smart-contract bounties and audit contests |  |
| Kevlar | Windows kernel-driver emulation & behavioral analysis (Unicorn) |  |
| Ophion | Intel VT-x research — EPT, VMCS and VM-exit interception, used for integrity and hypervisor-residency analysis |  |
| Ghidra MCP | Full Ghidra MCP (P-code, BSim, version tracking, emulation) |  |
| omniwire | Agent-swarm infrastructure — MCP, A2A, mesh VPN, browser automation |  |
| vibe-island | Native Dynamic Island HUD for AI coding agents |  |
| AiDA | IDA Pro 9.x plugin — AI-assisted reverse engineering |  |


- Game security & anti-cheat — cheat taxonomy, behavioral aim detection, match-integrity analytics
- Anti-cheat internals — kernel drivers, DMA hardware surface, hypervisor-level integrity research
- Cheat-community intelligence — trend monitoring and the intel → detection feedback loop
- Detection engineering — telemetry, SQL, explainable scoring, enforcement measurement
Open to game security / anti-cheat roles, detection engineering, RE / Windows internals work, and security-product engineering.
apex-anticheat-lab · Decepticon · GitHub · X · TryHackMe
while (true) { if (understand_the_cheat()) build_the_detection(); }